IoT Security for Enterprises.
Protect IP cameras, wireless access points, and connected enterprise devices from hardware & firmware vulnerabilities, unauthorized changes, and supply chain risk.
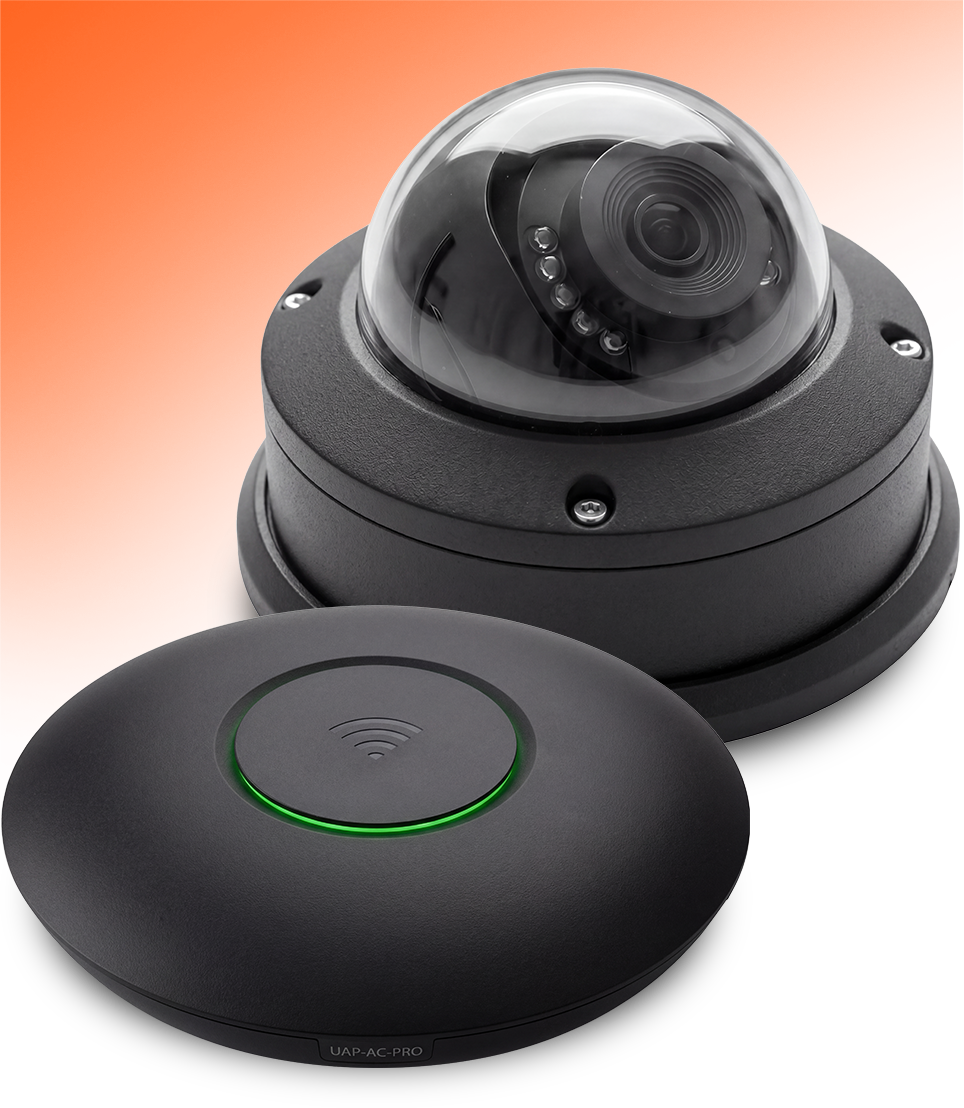
Enterprise IoT devices increasingly sit on the edge of the network, where they’re more exposed than core infrastructure. These devices aren’t covered by traditional vulnerability management or EDR. More compute power, intelligence, and data lives at the edge, making these devices an easier, and more valuable, and more vulnerable, target for cyberattackers.
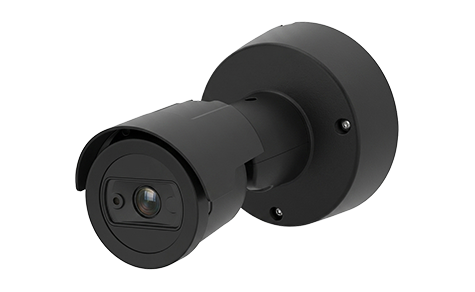
Traditional security tools were not built to inspect the firmware, embedded software, and hardware components inside Enterprise IoT devices.
Eclypsium provides continuous discovery, firmware and component-level visibility, integrity monitoring, and remediation support for connected devices that standard EDR, vulnerability scanners, and asset inventories don’t support.
Firmware and Component Visibility
Move beyond basic asset names and IP addresses.
Eclypsium helps security teams understand what is running inside connected devices, including firmware, embedded software, vendor components, and hardware measurements that traditional tools cannot inspect.
Integrity Monitoring and Threat Detection
Detect unexpected firmware changes, backdoors, implants, and signs of tampering across connected devices that cannot run endpoint security agents.
Vulnerability and Exposure Management
Continuously identify vulnerable firmware, insecure configurations, outdated software, exposed services, and device states that increase the likelihood or impact of compromise.
Remediation and Update Validation
Prioritize remediation based on device exposure and firmware risk. Validate firmware updates and confirm devices return to an expected state after remediation activities.
Enterprise IoT devices are often broadly deployed, remotely managed, and difficult to inspect with standard security tooling.
They are frequently trusted by the networks around them, but often lack the monitoring and remediation workflows applied to endpoints and servers.
IP cameras monitor entrances, offices, warehouses, production floors, data centers, parking lots, and restricted spaces.
A compromised camera can expose sensitive physical operations, support reconnaissance, or become a foothold inside the enterprise network. In some environments, cameras may also connect to access control, identity, video management, cloud storage, or physical security workflows, increasing the potential impact of compromise.
IP camera vulnerabilities are not theoretical. Advisories from the U.S. military and other nations have warned that camera flaws can allow remote attackers to compromise affected devices, gain control, or execute commands. Recent reporting has uncovered use of IP-camera hacking techniques as part of ongoing conflicts in Ukraine and Iran.
Wireless access points mediate network access for employees, guests, mobile devices, and connected systems.
A compromised WAP can put attackers near authentication flows, segmentation boundaries, user traffic, and device onboarding processes. Because WAPs are distributed throughout the enterprise, they also expand the number of locations where attackers may find exposed management interfaces, outdated firmware, or misconfigurations.
Many Enterprise IoT devices rely on firmware and embedded operating systems that are difficult for traditional security tools to inspect.
If attackers compromise these layers, they may gain persistence that survives reboots, resets, device reconfiguration, and even patching.
Enterprise IoT devices are often deployed outside data centers and away from central IT teams.
They may sit in hallways, ceilings, branch closets, factories, stores, clinics, parking lots, classrooms, and remote facilities. That distribution makes inventory, patching, monitoring, and validation harder.
Attackers benefit when defenders do not know what devices exist, what firmware they run, or whether those devices have drifted from a trusted state.
Enterprise IoT security requires visibility below the level where many security tools operate.
Standard endpoint and vulnerability management programs were designed for laptops, workstations, servers, and cloud workloads. They were not designed for fleets of embedded devices with vendor-specific firmware, inconsistent update processes, and limited monitoring options.

No Agents
Most Enterprise IoT devices cannot run EDR, endpoint management agents, or standard security tooling.
That leaves security teams dependent on external scanning, vendor portals, manual checks, or incomplete asset records.

Limited Firmware Visibility
A device inventory may show “Axis camera,” “Hikvision camera,” or “wireless AP,” but that is not enough to understand risk. Security teams need to know firmware versions, embedded components, exposed services, known vulnerabilities, and whether the device has changed unexpectedly.

Fragmented Ownership
Enterprise IoT often falls between teams. Physical security may own cameras. Networking may own WAPs. Facilities may own building systems. IT may own procurement. Security may own risk. Without a shared source of truth, remediation slows down.

Vendor-Specific Updates
Firmware updates are often different for every vendor, model, and deployment type. Security teams need to know which devices are affected, which updates are available, which systems should be prioritized, and whether updates were successfully applied.
Eclypsium helps organizations bring Enterprise IoT devices into the same security workflow used to protect endpoints, servers, network infrastructure, and AI hardware.
Eclypsium provides continuous discovery and inventory for connected devices across the enterprise, helping security teams find cameras, WAPs, and other embedded systems that may not appear in traditional endpoint inventories.
Eclypsium helps identify the details that matter for security, including device type, vendor, model, firmware version, hardware attributes, software components, and risk posture.
Enterprise IoT risk changes as new vulnerabilities are disclosed, vendors release firmware updates, and devices drift from approved configurations.
Eclypsium helps teams identify vulnerable firmware, insecure configurations, outdated software, unsupported devices, exposed services, and other risks before attackers exploit them.
With firmware and component-level context, teams can prioritize remediation based on operational risk and device exposure.
Enterprise IoT devices operate outside the reach of EDR.
Eclypsium helps close that detection gap by monitoring firmware and component integrity, establishing baselines, and identifying changes that may indicate tampering or compromise.
Security teams can detect unexpected firmware changes, backdoors, implants, and other signs of compromise across devices that cannot run endpoint security agents.

IP Camera Security
IP cameras are often deployed in large numbers across sensitive locations.
Eclypsium helps security teams understand which devices are present, which firmware they are running, and whether known vulnerabilities or integrity issues put the environment at risk.
Teams can identify vulnerable camera models and firmware versions, monitor for unexpected changes, and validate firmware updates across distributed physical security environments.

Wireless Access Point Security
Wireless access points are critical to network access and segmentation, but they are often difficult to inspect with endpoint-centric tools.
Eclypsium helps teams bring WAPs into the same security workflow as other connected embedded devices. Teams can identify firmware risk, insecure configurations, exposed management paths, outdated devices, and unexpected changes across distributed wireless infrastructure.

Branch and Remote Site Security
Branch offices, retail locations, schools, clinics, warehouses, and remote facilities often contain connected devices that are hard for security teams to see and patch.
Eclypsium helps extend firmware and component-level visibility to the distributed edge, where unmanaged Enterprise IoT risk can accumulate.

Procurement and Lifecycle Risk
Enterprise IoT risk begins before a device is installed.
Eclypsium helps organizations make more informed decisions about connected-device vendors, firmware, components, and long-term supportability. Teams can assess risk before deployment, monitor devices in production, and validate device state throughout the lifecycle.
Enterprise IoT Monitoring Requires Verification Beyond the Network
Security Control | What It Typically Monitors | What It Can Miss on IoT Devices | Where Eclypsium Adds Value |
|---|---|---|---|
Network vulnerability management | Reachable IPs, open ports, exposed services, banners, known CVEs, weak protocols | Embedded OS state, firmware components, modified firmware, hidden services, inaccurate version reporting, and devices that cannot tolerate active scans | Verifies firmware and component risk beyond what is visible from the network |
Passive IoT / OT discovery | Device identity, traffic patterns, protocols, manufacturer, model, and network behavior | Whether the firmware is authentic, whether components are vulnerable, whether the device has drifted from a known-good state, or whether unauthorized code is present | Adds device and firmware posture to passive network context |
EDR / XDR | Endpoint activity, processes, files, users, detections, and telemetry from agent-supported systems | Agentless devices such as IP cameras, printers, badge readers, appliances, unmanaged embedded systems, and network-connected hardware | Extends risk management and threat detection to devices that cannot run endpoint agents |
CMDB / asset inventory | Ownership, location, business context, lifecycle status, and manually maintained device records | Real-time firmware version, configuration drift, unauthorized modifications, and current exposure | Establishes a current device and firmware baseline and detects drift from that baseline |
Enterprise IoT risk changes over time as firmware updates, configuration drift, newly disclosed vulnerabilities, and operational changes affect deployed devices.
Eclypsium helps organizations protect connected devices across the full lifecycle.
During Onboarding
Evaluate device risk, firmware state, vendor exposure, and component-level security before new devices are introduced into the environment. Read more about how Eclypsium provides security during device onboarding.
In Production
Continuously monitor device posture, identify vulnerabilities, detect unexpected changes, and prioritize remediation based on risk. When updates or hardware refreshes occur, Eclypsium helps validate firmware updates and ensure devices return to a trusted state after changes are made. Read more about continuous monitoring of hardware in production.